

An AI assistant performs a task in 2 seconds. Testing is complete, and the pull request has been submitted.
Things are good in terms of speed but risky. DevSecOps teams will face the challenge of AI-generated code security on a daily basis by 2027. The statistics show as much as the skills that will fill the gap do.
Is AI-generated code safe?
Not by default. The GenAI Code Security 2025 Report, conducted by Veracode, included testing over 100 models and around 80 coding tasks. According to the analysis, roughly 45% of the cases involved bugs listed in the OWASP Top 10. Java’s performance was particularly disappointing – it had bugs in 70% of cases.
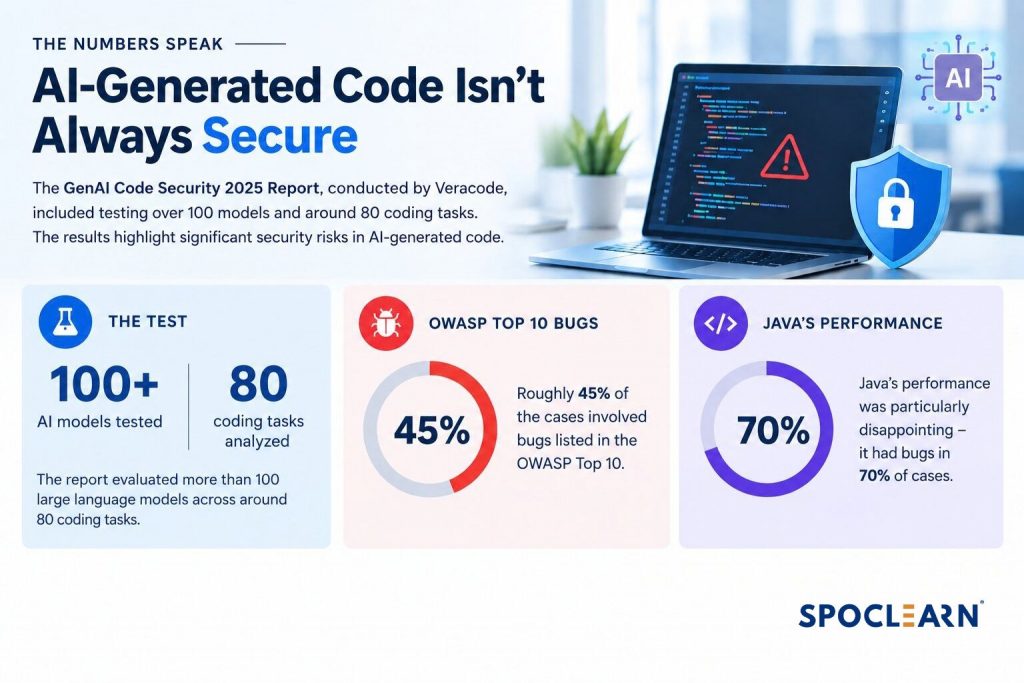
This data accounts for only confirmed findings. The general trend is the same – the models managed to defend themselves from cross-site scripting attacks in merely 14% of the cases.
Thus, weaknesses in AI-driven software development should be reflected in the present plans.
7 Essential DevSecOps Skills for Teams in 2027
The skills required for a DevSecOps engineer to manage AI-created programming code include:
- Secure prompting. Developers cannot create secure working code without specifying any security requirements. Therefore, one must understand concepts such as input validation, parameterized queries, etc.
- Security-oriented code reviewing. AI products should be treated as if they were written by a stranger. The process begins with authentication and input validation.
- Static analysis. Every commit must be audited to prevent vulnerabilities. Such practice is a common point of DevSecOps.
- Dependency checking. AI code must undergo software composition analysis to identify whether any vulnerable libraries have been used.
- Secrets and access management. It is crucial to keep keys secure outside prompts and repositories, and to grant AI agents minimal access.
- AI Threat Assessment. In 2029, Gartner anticipates that most successful attacks involving AI agents will relate to access management. This shows that this skill is very important.
- Control. You have to decide where AI-based programs can be used legally.
Where do these competencies originate?
First, it is important to obtain a widely recognized DevOps certification. Acquiring this certification will give you a common vocabulary with your team and demonstrate your professionalism to clients. For instance, the certification by Spoclearn is a two-day instructor-led DevSecOps Foundation program accredited by PeopleCert and does not require any prerequisites.
Second, practicing is important. You may choose to add a scanner to your pipeline or check an AI-generated PR against the security checklist.
FAQs
How to secure AI code?
Treat AI code as if it came from an untrustworthy source. Write security-led prompts. Make sure the final product has been vetted and the process has been checked for weaknesses. Include all dependencies slowly and one at a time.
What security threats does AI coding present?
AI code can promote bad practices or the use of insecure libraries. It is also at risk of prompt injection and hacking.
Is the DevSecOps certificate worth it?
DevSecOps certification will help you learn a common language and validate your skills, but it is not essential.