CRISC® Certification Training Course in Vietnam
 CN
 CN
 CN
 CN
Build the judgment to identify technology risk, evaluate controls and advise business leaders with CRISC® Certification Training in Vietnam. Spoclearn’s four-day, 32-hour instructor-led course follows ISACA’s current Certified in Risk and Information Systems Control examination framework. Learn risk governance, assessment, response, reporting and technology resilience through practical cases drawn from banking, fintech, software and industrial operations. Designed for experienced professionals and corporate teams in Ho Chi Minh City, Hanoi, Da Nang, Hai Phong and Can Tho.
Program Highlights
4-Day / 32-Hour Instructor-Led CRISC Examination Preparation
CRISC® Credential Governed and Awarded by ISACA
Aligned to the ISACA CRISC Examination Blueprint Effective November 3, 2025
Four Domains: Governance, Assessment, Response and Reporting, Technology and Security
Risk Registers, Control Effectiveness, KRIs and Practical Business Risk Scenarios
Live Virtual, Corporate On-site and Dedicated Team Training Arrangements

CRISC® CURRICULUM: COMPLETE COURSE SYLLABUS & LEARNING PATH
A - ORGANIZATIONAL GOVERNANCE
- Organizational Strategy, Goals, and Objectives
- Organizational Structure, Roles and Responsibilities
- Organizational Culture
- Policies and Standards
- Business Processes
- Organizational Assets
B - RISK GOVERNANCE
- Enterprise Risk Management and Risk Management Framework
- Three Lines of Defense Risk Profile
- Risk Appetite and Risk Tolerance
- Legal, Regulatory, and Contractual Requirements
- Professional Ethics of Risk Management
Eligibility
Quick answer, so you can get started with confidence.
- Three (3) or more years of experience in IT risk management and IS control. No experience waivers or substitutions.
Who Can Attend CRISC Training in Vietnam
Job roles that can take up CRISC training course include, but are not limited to:
- Business Analysts
- Risk Professionals
- Project Managers
- IT Professionals
- Chief Risk Officers (CROs)
- IT Audit Specialists
- Security Analysts
- Risk Consultants
- Compliance Officers
- Control Professionals
- Compliance Professionals
- Audit Managers
- IT Security Managers
- Governance Professionals
- Enterprise Risk Managers
- Operations Managers
- Chief Information Officers (CIOs)
- Anyone who manages a company’s IT risks and controls
What is CRISC Exam Pattern and Question Format?
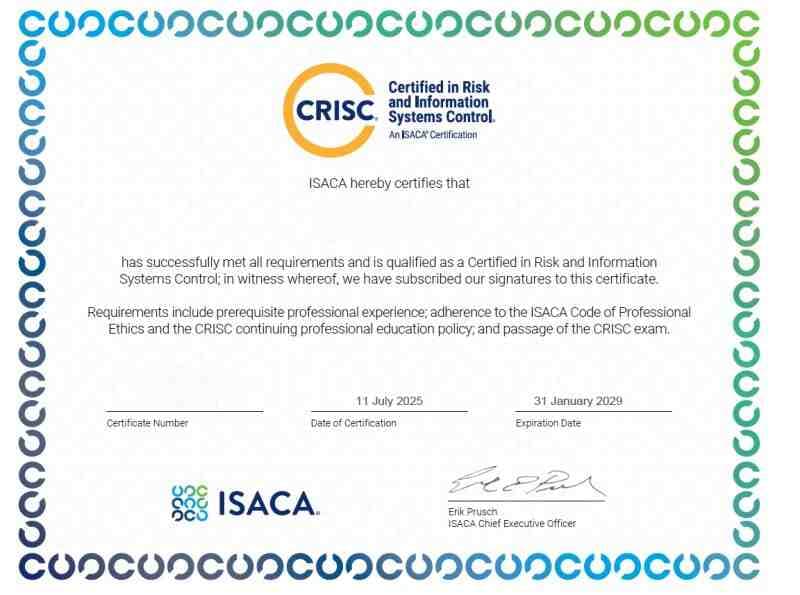
- Exam Type: Multiple-Choice Questions
- No. of Questions: 150
- Duration: 4 Hours (240 Mins)
- Passing score: 450 or Higher out of 800
- Languages: English, Chinese Simplified, Spanish, Korean.
Frequently Asked Questions
Certified in Risk and Information Systems Control (CRISC®) Certification Training in Vietnam
CRISC® Certification Training in Vietnam prepares technology risk, IT governance and control professionals to evaluate information systems exposure in business terms. Spoclearn’s 4-day, 32-hour program covers governance, risk identification and analysis, risk response, control design, monitoring, reporting, enterprise architecture and technology security. Learning follows ISACA’s four-domain framework, introduced on November 3, 2025, and encourages candidates to select proportionate risk responses rather than memorize control definitions.
In Vietnam, banks need confidence in digital payment availability, manufacturers must manage technology dependencies that affect production, and software providers face customer and supplier risks across borders. CRISC skills help professionals in Ho Chi Minh City, Hanoi, Da Nang, Hai Phong and Can Tho explain these exposures, document business ownership and challenge ineffective remediation plans. ISACA independently administers the exam and awards the credential after its experience and application requirements are satisfied.
16, 17, 18, 19 Nov 2026 (4 Days)
10:00 - 18:00 ICT(8 Hrs / Day)
Live Online Classroom
Included
Course Brochure
PDF · Curriculum, pricing & more
- Speak with an Expert
- Get Personalized Guidance
- Know More About Training
- Request a Corporate Proposal
Spoclearn: Training That Works for Corporates
Get tailored training programs for individuals and enterprise teams that help to maximize your training budgets
Customized training solutions designed to meet individual and organizational goals for maximum effectiveness.
Learn from 200+ global experts with real-world industry experience and proven expertise.
Blended training options to suit diverse learning preferences and geographically dispersed teams.
Post-training coaching ensures the practical application of skills for measurable, lasting results.
What Makes Spoclearn Different
Demand for CRISC Certification Training Across Ho Chi Minh City, Hanoi, Da Nang, Hai Phong and Can Tho
Why Enterprise IT Risk Management Matters in Vietnam
Vietnam’s financial services, technology outsourcing, manufacturing and digital commerce businesses rely on increasingly interconnected services. A customer transaction may depend on cloud infrastructure, a payment intermediary, identity systems and several external software components. Manufacturing facilities make a similar trade-off when equipment vendors can access production networks remotely. The difficulty is not merely finding vulnerabilities; it is deciding which dependencies threaten an important business outcome and who is accountable for the response.
A structured risk discipline helps leaders compare technical exposure with commercial consequences. Risk identification makes the scenario clear, assessment considers likelihood and impact, and treatment converts conclusions into practical action. CRISC preparation connects these steps to risk appetite, control effectiveness and reporting. It is useful for companies undergoing modernization, even where their internal risk framework differs from ISACA’s terminology.
2026 Regulatory and Cybersecurity Context
Vietnam’s Personal Data Protection Law, No. 91/2025/QH15, came into force on January 1, 2026. The Cybersecurity Law, No. 116/2025/QH15, followed on July 1, 2026. These laws are relevant to organizations assessing data processing, cybersecurity governance and technology-related obligations. The precise compliance duties depend on the organization’s sector, operating model, data and legal circumstances.
A CRISC-trained risk manager would not treat a statutory requirement as an optional risk to accept. Instead, the manager can identify which business processes and suppliers create exposure, assign responsible owners, assess controls and document remediation. Legal interpretation and regulatory assurance should remain with qualified specialists. The distinction matters because risk management supports compliance, but a training credential is not evidence of compliance.
Vietnam business development | Implication for IT risk and controls |
Personal Data Protection Law effective Jan 2026 | Data processing risk scenarios, accountable owners, vendor controls |
Cybersecurity Law effective Jul 2026 | Security governance, monitoring and response planning |
Growth of digital banking and payments | Third-party concentration, availability, integrity |
Industrial modernization | Operational technology, remote access, recovery |
Global software and supply chains | Contractual controls, client assurance, vendor monitoring |
Why Control Effectiveness Has Become a Management Concern
Organizations can have extensive security policies and still carry poorly understood exposure. An access control may exist on paper but fail when privileged accounts are not reviewed. A vendor contract may require incident notification without specifying workable escalation contacts. A recovery plan may contain targets that have never been tested. Risk professionals have to determine whether a control is actually operating as intended and whether the remaining exposure falls within acceptable limits.
CRISC covers risk response, control selection, testing methodologies, exceptions and ongoing monitoring. These responsibilities span IT, security, procurement, business operations and management. Stronger risk management becomes visible when unresolved exceptions have owners, technology investments are prioritized with evidence and executives receive risk information in terms they can act upon.
Practical Capabilities Vietnamese Enterprises Can Develop
Identify business-critical systems, data and third-party dependencies.
Build credible risk scenarios that connect threats with business impacts.
Define and document risk appetite, tolerance and escalation thresholds.
Evaluate inherent risk, control design, operational effectiveness and residual risk.
Distinguish risk reduction, sharing, avoidance and authorized acceptance.
Assign business risk owners and accountable control owners.
Monitor KRIs, KCIs and action progress using understandable dashboards.
Challenge unsupported exceptions and plans that fail to address root causes.
Incorporate cloud, AI, privacy and industrial resilience into risk reviews.
Produce concise, decision-ready risk reports for management.
CRISC Career Opportunities Across Vietnam
Technology risk professionals work where business objectives intersect with information systems, controls and external dependencies. A specialist may maintain a risk register, but a manager must also judge whether risks have been analyzed correctly, whether owners are empowered to respond and whether treatment is effective. The breadth of the role varies by company size and industry.
Relevant Career Opportunities
IT Risk Analyst and Senior IT Risk Analyst
Technology Risk Manager
IT Governance, Risk and Compliance (GRC) Manager
IT Controls Manager
Operational and Digital Resilience Manager
Third-Party Technology Risk Manager
Risk and Control Assurance Specialist
Cyber Risk Consultant
Enterprise Risk Manager with Technology Responsibility
Head of Technology Risk
CRISC Career Pathways Across Vietnam
Career role | Main responsibility | Relevant settings |
IT Risk Analyst | Risk scenarios, registers and assessment evidence | Hanoi, Ho Chi Minh City |
Technology Risk Manager | Treatment, reporting and control accountability | Banking, insurance, technology |
Third-Party Risk Manager | Vendor assessment and concentration exposure | Fintech, outsourcing, manufacturing |
IT Controls Manager | Control design, testing and exceptions | Financial services, industry |
Operational Resilience Manager | Critical services and recovery decisions | Banks, logistics, factories |
GRC Manager | Policy, risk and control governance | Hanoi, Ho Chi Minh City, Da Nang |
Head of Technology Risk | Portfolio-level exposure and executive challenge | Larger Vietnamese and multinational firms |
Career Progression Beyond CRISC
Career progression from risk analyst to head of technology risk usually requires broader exposure, not more complex spreadsheets. Senior managers are expected to identify how multiple systems create a shared failure scenario, challenge optimistic risk ratings, build treatment priorities and explain trade-offs to leaders outside technology. They also need experience in governance committees, crisis decisions and cross-functional delivery.
CRISC can support that path by developing a common discipline across governance, assessment, treatment and monitoring. It does not replace the experience required to manage people, budgets or enterprise decisions. Candidates should seek assignments that demonstrate a tangible reduction in uncertainty, clearer ownership and improved quality of control evidence.
Indicative Salary Snapshot: Vietnam, 2026
Adecco Vietnam’s Salary Guide 2026 provides occupational benchmarks for Hanoi and Ho Chi Minh City. For the broad “Head of Risk Management” position in financial services, the guide reports the gross monthly ranges shown below. They are a useful reference for senior risk leadership, but they are not salaries for CRISC-certified professionals specifically and should not be presented as an IT risk salary survey.
Location / occupation | Experience | Gross monthly salary (VND) |
Ho Chi Minh City – Head of Risk Management | 1–5 years | 90–110 million |
Ho Chi Minh City – Head of Risk Management | More than 5 years | 110–220 million |
Hanoi – Head of Risk Management | 1–5 years | 80–120 million |
Hanoi – Head of Risk Management | More than 5 years | 120–200 million |
Source: Adecco Vietnam Salary Guide 2026, Financial Services, page 27. These are job benchmarks, not CRISC certification premiums. Verify current vacancies and responsibilities for role-level comparisons.
Industries Requiring IT Risk and Information Systems Control Capabilities in Vietnam
Risk and control capabilities are relevant across sectors, but the business consequence of an IT incident differs sharply. For a bank, transaction integrity or customer access may be central. For a factory, several hours without operational systems could interrupt production. For a logistics provider, unreliable inventory data can disrupt delivery commitments even when no confidential data is lost.
Industry sector | Illustrative IT risk environment | Relevant locations |
Banking and financial services | Transaction integrity, data and outsourcing | Hanoi, Ho Chi Minh City |
Fintech and digital payments | APIs, platform availability and providers | Ho Chi Minh City, Hanoi |
IT outsourcing and software | Client obligations, identity and cloud controls | Da Nang, Ho Chi Minh City |
Manufacturing | Factory automation, maintenance access, production uptime | Hai Phong |
Telecommunications | Network resilience, service availability, suppliers | Hanoi |
Logistics and distribution | Warehouse systems, partner interfaces, recovery | Hai Phong, Can Tho |
E-commerce and retail | Customer information, payments, fraud controls | Ho Chi Minh City |
Healthcare | Sensitive data, clinical system availability | Hanoi, Ho Chi Minh City |
Energy and utilities | Service continuity and critical technology | Vietnam-wide |
Professional services | Client confidentiality and control assurance | Hanoi, Ho Chi Minh City |
Agriculture and food processing | Production traceability and distribution | Can Tho |
Public services and education | Citizen data, identity and availability | Vietnam-wide |
Selecting an Appropriate IT Risk Response
Risk treatment is not a contest to eliminate every possible threat. Organizations normally choose between reducing risk through controls, avoiding an activity, sharing or transferring elements of exposure, and accepting a level of residual risk through the appropriate authority. An insurance policy can help with financial consequences but does not necessarily remove operational disruption or accountability.
A cloud service used in Da Nang might justify stronger contractual requirements and independent recovery capacity. In Hai Phong, a production system may require manual fallback and tightly controlled supplier access. CRISC equips candidates to compare options using business impact, control evidence, decision rights and practical constraints.
CRISC Certification Opportunities Across Vietnam’s Major Cities
CRISC Certification Training and IT Risk Careers in Ho Chi Minh City
Ho Chi Minh City brings together banking, fintech, e-commerce, enterprise technology, logistics and multinational business operations. These organizations often rely on external payment providers, cloud environments and software partners. A seemingly small configuration change can create business exposure when ownership is fragmented across product, technology and supplier teams.
CRISC Certification Training in Ho Chi Minh City is relevant to professionals assessing those dependencies and translating findings into decisions. A risk analyst might challenge the completeness of an outsourcing assessment; a control manager could examine whether exceptions have valid business approval and a clear expiry date. The important skill is to show why risk matters to revenue, customers and continuity.
Ho Chi Minh City sector | Illustrative risk scenario | CRISC contribution |
Banking and fintech | Payment platform or partner failure | Risk assessment and treatment ownership |
E-commerce | Customer information leakage | Controls and residual risk reporting |
Multinational technology | Cloud provider concentration | Vendor and resilience risk |
Logistics | Integration error across distribution partners | Control design and monitoring |
Industrial operations | Remote support and network connectivity | Risk response and recovery oversight |
A fintech platform deploying a new payment partner might focus first on availability and transaction integrity. Its risk owner needs evidence about the partner’s controls and recovery capabilities, not simply a signed contract. In an e-commerce operation, similarly structured analysis may prioritize identity systems and customer data. Spoclearn’s CRISC preparation provides a setting to work through these contrasts.
Career pathways can include technology risk, GRC, third-party assurance and operational resilience. Applicants should compare actual role scope and seniority. Broad financial risk salary benchmarks are not direct forecasts for CRISC-certified IT risk professionals, and employment outcomes depend on responsibility and track record.
CRISC Certification Training and Technology Risk Governance in Hanoi
Hanoi’s banking, telecommunications, government-related services and large enterprise technology environments make risk governance and accountability significant responsibilities. Technology platforms support customer services and operational processes across many departments. A governance committee needs more than a list of unpatched systems; it needs to understand which assets are critical and what actions are proportionate.
For candidates considering CRISC Certification Training in Hanoi, the most useful cases involve risk appetite, control exceptions, outsourcing, network continuity and management reporting. A technology risk lead may be expected to challenge a proposed risk rating, while an audit professional moving into GRC may need to distinguish assurance findings from business-owned remediation decisions.
Hanoi business activity | Risk governance issue | Relevant CRISC practice |
Retail and commercial banking | Digital service and transaction exposure | Risk scenario assessment |
Telecommunications | Network disruption and dependencies | Business impact and resilience |
Government-linked services | Data, identity and continuity | Control selection and reporting |
Enterprise technology | Technology change and supplier issues | Risk response and exceptions |
Professional services | International client requirements | Control evidence and ownership |
Consider a bank introducing a new customer-facing application. Business and technology leaders must agree on acceptable downtime, data sensitivity, treatment funding and escalation. CRISC’s emphasis on risk governance ensures those questions are not left to a single engineer or a control checklist. An effective report identifies the scenario, owner, residual exposure and decision requested.
Risk managers in Hanoi may progress toward technology risk oversight, control management or broader enterprise risk roles. The professional advantage is strongest when candidates can demonstrate how their assessments changed decisions, rather than relying solely on course attendance or a credential.
CRISC Certification Training and Risk Management Opportunities in Da Nang
Da Nang has a significant software services, technology and hospitality business presence. Cross-border delivery creates risks involving client environments, project access, cloud contracts, data handling and operational continuity. An outsourcing provider may have excellent developers but still need credible risk assessments to demonstrate that client obligations are reflected in everyday controls.
CRISC Certification Training in Da Nang helps experienced practitioners examine those relationships. Risk scenarios can cover shared development tools, privileged access, a customer’s cloud dependency or the interruption of a reservation platform. Each requires a business impact assessment, a practical control response and a named owner who can make the relevant decision.
Da Nang activity | Potential technology exposure | Risk-management emphasis |
Software outsourcing | Access to external client environments | Contracts, controls and exceptions |
Cloud-hosted software | Infrastructure dependency | Concentration and resilience |
Hospitality technology | Booking and payment interruption | Business impact analysis |
Digital services | Personal data processing | Information risk and control ownership |
Industrial projects | Vendor-connected equipment | Supplier technology risk |
For example, a service provider with several overseas clients may use one identity platform for administration. The risk cannot be evaluated solely through authentication settings; the organization must examine business impact if the service fails, the ability to recover and the obligations owed to customers. CRISC gives a common structure for that assessment.
Potential career directions include technology risk consultant, GRC specialist and third-party assurance manager. Communication matters because the strongest assessment is ineffective if nontechnical stakeholders cannot understand the decision it requires. Live virtual CRISC training can make such practice available locally without relocation.
CRISC Certification Training and Industrial Risk Controls in Hai Phong
Hai Phong’s manufacturing, industrial and logistics economy creates technology risks that often directly affect physical operations. Modern plants rely on production scheduling systems, operational networks, machine interfaces and remote supplier support. Controls designed for ordinary office IT may not fit production equipment where downtime, safety and maintenance windows must be considered.
CRISC Certification Training in Hai Phong is useful for engineering IT managers, plant control owners, manufacturing risk specialists and internal audit teams. A sound assessment identifies the operating process at risk, the consequences of interruption, alternative procedures and the people authorized to approve mitigating actions. The objective is not to label every industrial vulnerability as critical.
Industrial scenario | Business impact | Relevant CRISC capability |
Remote vendor maintenance | Unauthorized access to plant systems | Third-party control ownership |
Production scheduling outage | Delayed manufacturing output | Business impact and treatment |
OT software update | Unexpected equipment interruption | Change and risk monitoring |
Port system integration | Service interruption and data errors | Control evaluation and resilience |
Warehouse automation | Order and shipment disruption | Technology and security risk |
Imagine a production line that requires a specialist vendor to perform remote diagnostics. Completely removing access may be impractical, while unrestricted connectivity is unacceptable. The relevant response might combine controlled approval, strong authentication, monitoring and tested restoration. CRISC encourages a comparison of those options against real operational requirements.
Professionals can apply these skills in factory IT governance, industrial risk management, supplier control oversight and business continuity. The credential complements rather than replaces safety engineering, operational technology expertise or the regulatory responsibilities attached to particular industrial operations.
CRISC Certification Training and Operational Risk Management in Can Tho
Can Tho serves agricultural, food-processing, distribution, trade and regional service activities in the Mekong Delta. Businesses may rely on cold-chain monitoring, inventory platforms, warehouse systems, supplier connections and financial applications. An IT failure can affect product quality or delivery commitments even where information confidentiality is not the principal issue.
CRISC Certification Training in Can Tho gives operations and technology professionals a way to evaluate these business consequences. A distribution manager may need to know how long dispatch can continue without the warehouse system. A food-processing business may examine the integrity of traceability records and the ability to restore production data.
Can Tho business segment | Risk scenario | CRISC response focus |
Food processing | Production or traceability outage | Control and recovery assessment |
Cold-chain logistics | Monitoring data disruption | Business impact and resilience |
Agricultural supply chain | Vendor data and access dependencies | Supplier risk governance |
Regional retail | Payment and stock system interruption | Risk treatment priorities |
Service providers | Customer information exposure | Risk ownership and reporting |
For a cold-chain operator, the most important risk may be an inability to monitor temperatures during a network interruption. A sensible response could involve local recording, escalation triggers and a manual procedure tested in advance. This differs from the control priorities of a city-based software business, but the underlying risk process remains similar.
Potential roles include IT controls manager, operational resilience coordinator and regional technology risk specialist. Live instructor-led training can accommodate professionals in Can Tho while keeping course examples connected to practical business conditions. Exam and certification decisions remain with ISACA.
How CRISC Professionals Support Vietnamese Enterprises
Effective risk managers do not simply count findings. They establish whether a reported exposure matters to an enterprise objective, how it is controlled, who is accountable and whether the remaining risk can be accepted. These decisions require evidence, a clear understanding of business priorities and the confidence to challenge an overly reassuring assessment.
Enterprise Challenges and CRISC Capabilities
Enterprise challenge | CRISC-related capability | Practical management outcome |
Risks described only as technical issues | Risk scenarios and business impact | Meaningful prioritization |
Unclear decisions about exceptions | Risk appetite and approval rights | Documented accountable owners |
Controls exist but are not operating | Control design and effectiveness review | Evidence-based remediation |
Vendor risk is poorly understood | Third-party assessment and monitoring | Visibility of critical dependencies |
Risks are ranked inconsistently | Assessment methods and calibration | More comparable risk results |
Reporting overwhelms executives | KRIs, dashboards and action tracking | Clearer risk decision requests |
Continuity plans remain untested | Resilience and recovery assessment | Better operational preparedness |
Practical Contributions of CRISC Professionals
Review material technology risks against current business objectives.
Challenge likelihood, impact and control-effectiveness assumptions.
Build cross-functional risk registers with accountable owners.
Prioritize treatment plans using business impact and risk appetite.
Evaluate control exceptions, waivers and overdue actions.
Review supplier concentration and recovery dependencies.
Translate technical evidence into board-ready risk communication.
Coordinate risk reporting across IT, security, compliance and operations.
A risk manager’s credibility grows when reports lead to useful decisions. An unresolved high-risk condition should not simply roll over into the next month’s dashboard. It should have a business owner, a response decision, a realistic timetable and evidence of progress. This approach turns technology risk management from periodic documentation into ongoing enterprise governance.
CRISC for Digital Transformation, AI, Privacy and Resilience in Vietnam
CRISC Applications in Modern Enterprise Technology
Vietnamese enterprises are introducing cloud services, API ecosystems, automation and customer-facing digital products. Each development changes the risk profile: a service can become dependent on a small number of cloud regions, a supplier can gain access to sensitive operational data, or a minor integration error can affect thousands of transactions. CRISC helps organize assessment and oversight when technical architecture is changing faster than existing policy.
Technology change | Key IT risk question |
Cloud migration | Which provider and recovery dependencies matter most? |
Digital payments | Who owns failure, fraud and integrity exposure? |
Industrial IoT | What business interruption is tolerable? |
Outsourced development | How are contractual controls tested? |
AI-assisted decision support | How are data, model and misuse scenarios evaluated? |
Regional shared services | How is concentration risk monitored? |
Managing AI and Automation Risk
AI-enabled tools may introduce risks involving data quality, confidentiality, inappropriate output, unclear accountability or reliance on a single external provider. Risk managers should first identify the business decision being supported, the harm that could follow from a failure and the controls available to reduce that exposure. Technical accuracy is only one part of the assessment.
A financial services company in Ho Chi Minh City may use AI in customer service or fraud investigations. The relevant CRISC questions involve authorization, data handling, oversight and escalation when outputs are unreliable. In a manufacturing setting, automation can create different consequences related to availability and physical operations. Specialist model assurance may be needed alongside enterprise risk governance.
Privacy and Vietnam’s Regulatory Environment
The 2026 legal environment increases the importance of treating personal information and cybersecurity obligations as managed business responsibilities. Risk professionals need to know which processes handle regulated data, whether control owners understand relevant obligations and how suppliers support or undermine those obligations. They should also be able to document risk assessments without creating unnecessary exposure in the evidence collected.
CRISC provides a structure for identifying, responding to and reporting relevant IT risk, but a professional certification does not replace legal advice, privacy engineering or a compliance assessment. Each organization should confirm which Vietnamese legal provisions apply to its particular operations and the deadlines for required actions.
Business Continuity and Technology Resilience
A good resilience assessment starts with the service the business must continue, not the backup product it owns. A bank might prioritize access to payment services; a manufacturer might focus on production control; a distributor may need order and inventory visibility. Business impact analysis then supports decisions about recovery time, alternate procedures and testing priorities.
CRISC candidates should understand how technology dependencies affect these choices. Risk treatment may require redundancy, supplier arrangements, manual fallback or management-approved exposure. Recording the residual risk and testing the response make resilience plans more credible than simply listing systems that have been backed up.
Risk Governance in Agile, DevOps and Rapid Technology Change
Organizations that release software frequently cannot rely on annual risk reviews as their only control. Risk owners need appropriate checkpoints around architecture changes, privileged access, production deployment and supplier connections, together with thresholds for escalating material exceptions. The aim is to make risk decisions timely without turning every small change into an executive approval.
CRISC’s framework supports a risk-based approach to technology operations and system development. In Da Nang’s software delivery environments, teams can combine automated control evidence with documented ownership and regular review. In Ho Chi Minh City’s fintech sector, the same principles can guide controls around integrations and platform changes.
Benefits of CRISC Certification for Professionals in Vietnam
CRISC can help experienced professionals turn scattered knowledge of technology risk into a coherent approach to governance, assessment, treatment and reporting. Its value is particularly visible when a practitioner must explain a technical exposure to a business leader who is responsible for an investment or operational decision.
Key Professional Benefits
Develops a structured vocabulary for enterprise IT risk and systems controls.
Strengthens assessment of inherent and residual exposure.
Supports better choices about risk response and control effectiveness.
Improves communication with business owners, auditors and executives.
Connects security, operations and third-party risks to enterprise objectives.
Provides an internationally recognized ISACA credential when certified.
Supports career development in GRC, technology risk and resilience.
Encourages ongoing professional learning through ISACA maintenance requirements.
CRISC Skills for Different Professional Groups
Professional group | Most useful CRISC emphasis |
IT risk analysts | Scenario analysis, registers and reporting |
Information security professionals | Business impact and response decisions |
IT auditors | Risk treatment and control ownership |
GRC and compliance specialists | Frameworks, risk governance and exceptions |
Technology managers | Architecture, change and resilience risk |
Vendor managers | Supplier exposure and ongoing monitoring |
Future technology risk leaders | Risk appetite, enterprise communication and oversight |
Benefits of Corporate CRISC Training for Vietnamese Organizations
A shared understanding of technology risk makes decisions easier to coordinate across departments. Security can explain threats; operations understands service dependencies; procurement manages supplier terms; finance evaluates investment; and business management owns the consequences. CRISC preparation is most useful when it helps these groups discuss one risk scenario using a consistent set of assumptions and evidence.
Corporate CRISC Training Benefits by Department
Department / stakeholder | Potential training application |
Enterprise risk management | Integrated technology risk profile and appetite |
IT and cybersecurity | Risk-based control prioritization |
Internal audit | Clearer distinction between assurance and ownership |
Procurement / vendor management | Critical third-party risk oversight |
Operations and continuity | Business impact and recovery priorities |
Privacy and compliance | Evidence of control responsibilities |
Executive leadership | Concise residual risk and action reporting |
Measuring Corporate CRISC Training Effectiveness
Suggested measure | Before-and-after check |
Material risk ownership | Percentage with named, approved owners |
Assessment quality | Completeness of scenario, impact and control evidence |
Treatment progress | Aging and closure of risk action plans |
Vendor oversight | Coverage of critical supplier reviews |
Executive reporting | Frequency and clarity of decision-ready risk reports |
Exception governance | Share of exceptions with approved expiry dates |
From Individual Learning to Organizational Risk Capability
After training, a company can select two or three material technology exposures and review them using the same discipline taught in the classroom. Participants might refresh an outdated business impact assessment, challenge a supplier risk rating, validate an ineffective control or simplify a risk report for the executive committee. These limited projects create evidence of whether the training is changing practice.
Management sponsorship is essential. A well-documented risk that lacks an accountable owner will remain unresolved. The company should give trained participants authority to coordinate evidence, ask difficult questions and raise issues when actual exposure falls outside agreed tolerance. That is where an investment in CRISC capability begins to support business resilience.
Upcoming CRISC Training Schedule in Vietnam
Spoclearn offers instructor-led CRISC examination preparation for individual professionals and corporate teams across Vietnam. Public-batch dates, Vietnam-local session times, instructor availability, fees and training language should be confirmed through the live schedule or with a training advisor. Static content should not present unverified upcoming dates as confirmed places.
Training format | Duration | Location / arrangement | Action |
Live virtual public batch | 4 days / 32 hours | Vietnam-local scheduling; subject to availability | View Training Schedule |
Private live virtual cohort | 4 days / 32 hours | Company-specific cohort across Vietnam | Request Corporate Proposal |
Corporate on-site program | 4 days / 32 hours | Selected Vietnam location by arrangement | Discuss On-site Delivery |
Enrollment checklist: confirm that materials match the current CRISC blueprint, verify instructor experience, training language, timetable, exam voucher treatment, fees and cancellation terms.
Build Stronger Enterprise IT Risk and Control Capabilities Across Vietnam
CRISC Certification Training equips experienced professionals to identify technology-related business exposure, evaluate controls, propose workable responses and report residual risk with clarity. Across Ho Chi Minh City, Hanoi, Da Nang, Hai Phong and Can Tho, Spoclearn’s 4-day, 32-hour program provides structured preparation for ISACA’s current risk and information systems control examination.
Enroll in an available instructor-led batch or request a dedicated corporate training proposal built around your organization’s technology risk environment. ISACA independently administers the examination and awards the professional credential only after applicants meet its experience, application and maintenance requirements.
Where CRISC® Holders Drive Success
Request a Call Back from Spoclearn – We’re Just a Click Away
Got questions or need help choosing the right training or consulting solution? Schedule a call back with our expert team whenever you're able. Select a time that suits your schedule, and we’ll reach out to guide you through your options.