CISM® Certification Training Course in Vietnam
 CN
 CN
 CN
 CN
Move from managing security tools to leading enterprise security decisions with CISM® Certification Training in Vietnam. Spoclearn’s 4-day, 32-hour instructor-led program covers ISACA’s updated November 2026 CISM framework, helping security professionals strengthen governance, information security risk management, security program leadership and incident readiness. Designed for experienced professionals and corporate teams across Ho Chi Minh City, Hanoi, Da Nang, Hai Phong and Can Tho.
Program Highlights
4-Day / 32-Hour Instructor-Led CISM Examination Preparation
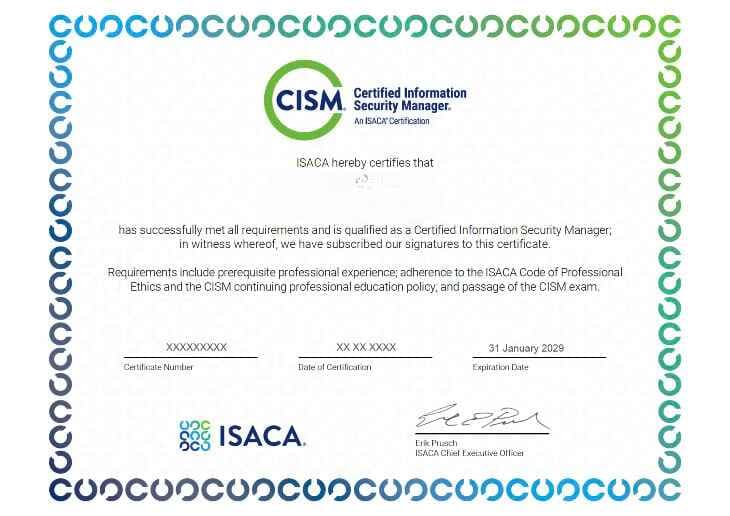
CISM® Credential Governed and Awarded by ISACA
Aligned to the Updated November 2026 CISM Examination Outline
Four Domains: Governance, Risk, Security Program and Incident Management
Management Scenarios for Vietnam’s Banks, Technology and Industrial Sectors
Live Virtual, On-site and Corporate Team Training Arrangements

CISM CURRICULUM: COMPLETE COURSE SYLLABUS & LEARNING PATH
A – ENTERPRISE GOVERNANCE
- Organizational Culture
- Legal, Regulatory and Contractual Requirements
- Organizational Structures, Roles and Responsibilities
B – INFORMATION SECURITY STRATEGY
- Information Security Strategy Development
- Information Governance Frameworks and Standards
- Strategic Planning (e.g., Budgets, Resources, Business Case)
Eligibility
Quick answer, so you can get started with confidence.
- Five (5) or more years of experience in information security management. Experience waivers are available for a maximum of two (2) years.
Who Can Attend CISM Training in Vietnam
Job roles that can take up CISM training include, but are not limited to:
- IT Professionals
- Cybersecurity Experts
- IT Auditors
- Risk Managers
- Compliance Officers
- Security Consultants
- IT Governance Professionals
- Network Security Managers
- Information Security Analysts
- Security Architects
- Chief Information Security Officers (CISOs)
- Ideal for individuals who have experience managing, designing, overseeing, and assessing an enterprise's information security program
- Professionals to boost information security management careers and broaden their knowledge of global security practices
What is CISM Exam Pattern and Question Format?
- Exam Type: Multiple-Choice Questions
- No. of Questions: 150
- Duration: 4 Hrs
- Passing score: 450/800
- Languages: English, Chinese Simplified, Japanese, Spanish, Turkish.
Frequently Asked Questions
Certified Information Security Manager (CISM) Certification Training Across Vietnam
CISM® Certification Training in Vietnam prepares experienced cybersecurity, information risk and IT governance professionals to lead information security as a business function. Spoclearn’s four-day, 32-hour program explores strategy, risk appetite, policy ownership, program investment, security architecture, third-party oversight, incident response and recovery. The course follows ISACA’s current CISM job-practice outline, effective November 3, 2026, and uses management-focused case discussions rather than concentrating only on technical controls.
Organizations across Vietnam are navigating cloud adoption, digital payments, industrial connectivity, outsourced technology and rising privacy and cybersecurity obligations. A financial institution in Hanoi may need clearer risk reporting, while a manufacturer in Hai Phong may prioritize operational recovery and access to suppliers. For professionals in Ho Chi Minh City, Da Nang and Can Tho, CISM preparation provides a structured way to make security decisions understandable to business leaders. ISACA independently administers the examination and awards certification only after its applicable requirements are met.
16, 17, 18, 19 Nov 2026 (4 Days)
10:00 - 18:00 ICT(8 Hrs / Day)
Live Online Classroom
Included
Course Brochure
PDF · Curriculum, pricing & more
- Speak with an Expert
- Get Personalized Guidance
- Know More About Training
- Request a Corporate Proposal
Spoclearn: Training That Works for Corporates
Get tailored training programs for individuals and enterprise teams that help to maximize your training budgets
Customized training solutions designed to meet individual and organizational goals for maximum effectiveness.
Learn from 200+ global experts with real-world industry experience and proven expertise.
Blended training options to suit diverse learning preferences and geographically dispersed teams.
Post-training coaching ensures the practical application of skills for measurable, lasting results.
What Makes Spoclearn Different
Demand for CISM Certification Training Across Ho Chi Minh City, Hanoi, Da Nang, Hai Phong and Can Tho
Why Cybersecurity Management Is Becoming a Business Priority
Vietnam’s banks, digital commerce businesses, software providers and industrial exporters operate across larger technology ecosystems than they did only a few years ago. Core systems connect to cloud services, mobile applications, software suppliers, logistics platforms and remote employees. This increases the number of decisions that cannot be delegated solely to a technical security team. Someone must decide which risks the organization can accept, which controls deserve funding and how security incidents will affect customers or production.
Vietnam’s 2026 employment data also illustrates a market looking for experienced technology leaders. Adecco’s Vietnam Salary Guide 2026 highlights selective recruitment for professionals who can deliver immediate impact in digital transformation, regulation and technical management. This observation does not measure CISM-certified job vacancies specifically; it provides context for why information security leadership is relevant to organizational performance.
2026 Regulatory and Cybersecurity Context
Vietnam’s Law on Personal Data Protection No. 91/2025/QH15 and Decree 356/2025/ND-CP took effect on January 1, 2026. The country’s 2025 Cybersecurity Law, which consolidates earlier cybersecurity and cyberinformation security legislation, took effect on July 1, 2026. Requirements vary according to organizations, sectors, information and activities; businesses should seek appropriate legal guidance rather than assume all obligations apply identically.
For information security managers, these developments underscore practical questions: Who owns regulated information? Which suppliers process it? What response process applies to an incident? How is evidence preserved? Who reports risks to management? CISM’s governance and risk domains help organize these questions, while its program and incident-management domains address execution. The certification is not a Vietnamese legal-compliance approval.
Current Vietnam context | Management implications |
Personal Data Protection Law (Jan 2026) | Data ownership, classification, protection and vendor oversight |
Cybersecurity Law (Jul 2026) | Security accountability, preparedness and response coordination |
Digital payments and cloud adoption | Third-party risk, monitoring and recovery arrangements |
Industrial connectivity | Availability, remote access and operational risk |
International service contracts | Client security assurance and reporting |
Why Security Management Matters to Vietnamese Enterprises
Security failure often reflects a decision problem before it becomes a technology problem. A company may buy monitoring software but leave alert escalation unclear. It may outsource a cloud platform without assigning a risk owner, or test backups without confirming that the business can resume critical services. CISM-trained managers learn to identify these gaps between controls and accountability.
Translate enterprise objectives into a realistic information security strategy.
Define accountable security, control and business risk owners.
Prioritize security investment using business impact and risk appetite.
Oversee policy implementation, security architecture and third parties.
Select meaningful program performance and risk indicators.
Plan and exercise incident response, crisis communication and recovery.
Improve governance between IT, operations, compliance and executives.
These capabilities have different applications in Hanoi’s financial services industry, Ho Chi Minh City’s technology and commerce businesses, Da Nang’s software sector, Hai Phong’s industrial operations and Can Tho’s supply-chain economy.
CISM Career Opportunities Across Vietnam
CISM is intended for professionals who are accountable for how security is managed, not simply how individual controls are configured. Relevant careers encompass information security strategy, risk management, third-party oversight, program execution and incident leadership. Roles differ by company size: an SME Security Manager may own both governance and operations, while a large financial group may divide responsibilities among specialized teams.
Relevant Career Opportunities
Information Security Manager
Cybersecurity Manager
IT Security Governance Manager
Information Security Risk Manager
Security Program Manager
Governance, Risk and Compliance (GRC) Manager
Third-Party Security Risk Manager
Information Security Consultant
Security Operations Manager with governance responsibility
Head of Information Security
Deputy CISO or Chief Information Security Officer
CISM Career Pathways Across Vietnam
Career role | Principal responsibility | Relevant Vietnam business environments |
Information Security Manager | Strategy, controls and security ownership | Hanoi, Ho Chi Minh City |
Security Risk Manager | Assessment, treatment and reporting | Banking and enterprise technology |
GRC Manager | Policies, risk and assurance coordination | Financial services, IT outsourcing |
Security Program Manager | Security projects, resources and metrics | Technology, telecommunications |
Industrial Security Manager | Operational and cyber resilience | Hai Phong and industrial clusters |
Head of Information Security | Business-aligned security leadership | Vietnam-wide larger enterprises |
CISO | Executive security governance and crisis accountability | Major banks, technology and multinational firms |
Career Progression Beyond CISM
A useful path from technical leadership to executive responsibility is built through progressively larger decisions. A team lead may organize incident handling; a security manager may own program budgets and risk reporting; a Head of Security may coordinate business units; and a CISO may regularly advise executives or directors. Experience communicating difficult trade-offs matters as much as technical knowledge.
CISM provides a recognized management knowledge framework for this development. It does not shorten the years required to build trust, lead a workforce or navigate sector-specific regulatory issues. Professionals in Vietnam should use it as one element of a career plan combining job responsibility, mentoring, current technical awareness and evidence of measurable results.
Indicative Salary Snapshot: Vietnam, 2026
Adecco Vietnam’s 2026 survey reports Cyber Security Manager gross monthly salaries in Hanoi at VND 50–80 million for one to five years of experience and VND 60–120 million above five years. It does not publish Ho Chi Minh City figures in that same occupational row. These numbers describe market occupations, not a CISM salary premium, and are best used as a reference point rather than an individual offer prediction.
Location / role | Experience | Indicative gross monthly salary |
Hanoi – Cyber Security Manager | 1–5 years | VND 50–80 million |
Hanoi – Cyber Security Manager | More than 5 years | VND 60–120 million |
Ho Chi Minh City – same role | No range in Adecco row | Use live role-specific benchmarks |
Industries Requiring Information Security Management Capabilities in Vietnam
Information security leadership is needed wherever information, technology-dependent services or operational processes create material business exposure. The right security program must reflect industry conditions: manufacturing organizations may prioritize uptime, banks may emphasize transaction integrity and privacy, and software providers may need strong evidence for customer security reviews.
Industry sector | Illustrative security management priorities | Relevant Vietnam locations |
Banking and financial services | Risk governance, digital payment protection, outsourcing | Hanoi, Ho Chi Minh City |
Technology and software outsourcing | Client security programs, cloud and access control | Da Nang, Ho Chi Minh City |
Telecommunications | Service resilience, supplier risk, infrastructure security | Hanoi |
Industrial manufacturing | Operational technology, continuity, remote maintenance | Hai Phong |
Logistics and distribution | Vendor access, availability and recovery | Can Tho, Hai Phong |
E-commerce and retail | Customer information and payment ecosystem | Ho Chi Minh City |
Healthcare | Sensitive data, continuity and operational controls | Hanoi, Ho Chi Minh City |
Education and public services | Identity, data governance and service continuity | Vietnam-wide |
Energy and utilities | Critical service resilience and incident coordination | Vietnam-wide |
Professional and consulting services | Client assurance, policies and third-party control | Hanoi, Ho Chi Minh City |
Selecting the Right Security Management Approach
A security program should start with the business’s critical assets and risk appetite, not a predetermined list of technologies. A fintech firm may need rapid monitoring of transaction exposure. A manufacturer may need recovery plans that account for physical equipment. A cross-border software provider may need contractual assurance and supplier governance. CISM helps managers adapt their program to these different outcomes.
CISM Certification Opportunities Across Vietnam’s Major Cities
CISM Certification Training and Cybersecurity Careers in Ho Chi Minh City
Ho Chi Minh City is a major centre for banking, payments, retail technology, cloud services, industrial investment and international business. With technology dependencies spread across vendors and locations, security leaders must be able to explain cyber risk in commercial terms. CISM Certification Training in Ho Chi Minh City supports experienced professionals who want to manage enterprise security programs and incident readiness rather than remain limited to individual technical tasks.
Following the 2025 administrative restructuring, the expanded city encompasses the former Binh Duong and Ba Ria–Vung Tau areas, adding substantial manufacturing and port-related operations to the larger metropolitan context. This makes the relationship between corporate IT, supplier access and operational continuity particularly important. A security policy created for a financial application cannot simply be copied into an industrial plant.
Local business sector | Illustrative security challenge | Relevant CISM capability |
Fintech and banking | Third-party payments and customer data | Governance, risk acceptance |
Technology services | Cloud supplier and privileged access | Security program ownership |
Manufacturing | Industrial systems and downtime exposure | Risk and recovery planning |
Retail and e-commerce | Customer information and account takeover | Control oversight, incident handling |
Consider a digital payment provider preparing to launch a service through several technology partners. Its security leader needs to define ownership of risk assessments, vendor assurance, response communications and service recovery. CISM training develops the management reasoning behind those choices, including when business leaders must approve residual risk rather than leaving it to a technical specialist.
Professionals targeting CISM training in Ho Chi Minh City may work in information security, technology risk, IT governance, GRC, security operations or consulting. Career progression is strongest when they can show successful decisions, stakeholder influence and effective program delivery. ISACA certifies qualifying professionals after the independent exam and verified experience process.
CISM Certification Training and Information Security Leadership in Hanoi
Hanoi combines major banking, telecommunications, technology, government administration and professional services activities. These organizations often have formal governance structures and significant expectations for secure information handling. CISM Certification Training in Hanoi is relevant to professionals responsible for security policy, risk reporting, control ownership and crisis preparation across business and technology departments.
The 2026 data protection and cybersecurity framework adds further reasons for organizations to understand which security obligations apply to their operations. Managers need a disciplined process for assessing requirements and coordinating legal, compliance and technical teams. CISM provides a general management structure for those conversations, but neither the course nor the credential provides a legal opinion or substitutes for sector-specific compliance assessments.
Hanoi activity | Management issue | CISM application |
Banking and finance | Security risk reporting and third parties | Governance and risk domain |
Telecommunications | Service disruptions and infrastructure dependencies | Incident management |
Enterprise technology | Policies and security investment | Security program |
Professional services | Client assurance and data access | Governance and control oversight |
A bank changing its core platform may have several vendors, migration deadlines and operational constraints. A security manager should document the risks that matter to the business, identify accountable owners and ensure incident responsibilities remain clear during the transition. Training helps participants practise such decisions using scenarios in which perfect technical solutions may not be commercially or operationally feasible.
Adecco Vietnam’s 2026 salary guide lists Hanoi Cyber Security Manager benchmarks of VND 50–80 million and VND 60–120 million gross monthly for its two experience categories. These are job-market figures rather than compensation guaranteed by CISM. Professionals should compare the authority and experience demanded by each vacancy.
CISM Certification Training and Security Program Management in Da Nang
Da Nang has a strong software development, technology services, tourism, education and digital business presence. The expanded city following the 2025 administrative restructuring also includes the former Quang Nam area, widening its industrial and regional business profile. CISM Certification Training in Da Nang helps security leads understand how a program should protect customer commitments, operations and long-term business value.
International software services bring security questions that are often management questions: what evidence should be supplied to overseas customers, who approves cloud access, which subcontractors can see client information and what happens when a release creates unexpected exposure? Security leads must understand agreements, risk ownership and operational readiness alongside application security practices.
Da Nang business area | Illustrative risk | Management priority |
Software outsourcing | Client environment access | Policy and contract ownership |
Cloud platforms | Supplier concentration | Risk treatment and resilience |
Hospitality technology | Customer information exposure | Program oversight |
Industrial development | Connected plant systems | Incident and recovery readiness |
A software provider delivering for an international customer may discover that a third-party tool retains sensitive project information. The security manager must determine the business impact, coordinate contractual and technical responses, document the decision and update supplier controls. CISM’s governance, risk and program domains provide a practical way to approach that responsibility.
Professionals seeking CISM training in Da Nang can use a live virtual four-day batch to study alongside peers from larger commercial centres. Experience in vendor management, cloud governance and security reporting can strengthen a move from technical execution into a client-facing management role.
CISM Certification Training and Industrial Cybersecurity Management in Hai Phong
Hai Phong is an industrial, logistics and port-related centre in northern Vietnam. Its 2025 administrative expansion incorporated the former Hai Duong area, increasing the breadth of its manufacturing operations. CISM Certification Training in Hai Phong is relevant to leaders overseeing security around production systems, industrial connectivity, supplier access and business recovery.
A plant may depend on production equipment that cannot be patched on the same timetable as office laptops. Stopping a line can have direct commercial and safety consequences. Information security managers must work with operations, engineering and vendors to choose controls that reflect these constraints. CISM encourages risk-based decisions rather than assuming every environment should use the same technical security baseline.
Industrial scenario | Management decision | CISM domain |
Remote maintenance access | Approve, monitor and review vendor privileges | Risk / program |
Ransomware affecting production | Escalation and business recovery order | Incident management |
Plant network modernization | Security architecture and budget | Governance / program |
Supplier IT integration | Risk ownership and contractual controls | Governance / risk |
A ransomware incident affecting production planning could require containment, communication with management, validation of recovery options and coordination with suppliers. The security manager may not personally rebuild the systems, but must ensure responsibilities, escalation and business priorities are understood. That distinction makes CISM particularly useful for experienced industrial IT and security leaders.
Potential career paths include Industrial Security Manager, Security Program Manager, IT Risk Manager and Head of Information Security. The strongest candidates combine plant or engineering knowledge with sound security governance and incident leadership.
CISM Certification Training and Operational Resilience in Can Tho
Can Tho is a commercial centre in the Mekong Delta, with business activity across food processing, agriculture, logistics, distribution, retail and regional services. Following the 2025 administrative restructuring, the enlarged city includes the former Hau Giang and Soc Trang areas, increasing its industrial and supply-chain reach. CISM Certification Training in Can Tho helps managers address the security risks associated with connected regional operations.
A food-processing business may depend on cold storage monitoring, supplier systems, distribution scheduling and inventory databases. An outage in one service can affect the others. Security managers therefore need to know which systems are truly critical, what downtime is tolerable, who should approve a workaround and how the business will communicate disruption.
Can Tho sector | Information security exposure | Relevant CISM skill |
Food processing | Production and monitoring-system outage | Continuity planning |
Agriculture supply chains | Third-party access and system data | Vendor risk governance |
Logistics | Availability of dispatch and inventory systems | Incident preparedness |
Regional retail | Customer data and payment applications | Security program controls |
Consider a distribution firm whose scheduling system becomes unavailable during peak demand. A technical team can restore servers, but the security manager must coordinate priorities, risk communication and recovery decisions with operations. CISM training explores those cross-functional responsibilities and the need to test plans before a real incident.
For professionals in Can Tho, a live virtual cohort can provide access to management-level learning without unnecessary travel. The credential is internationally consistent, while the practical value comes from applying the framework to the region’s actual industry and business risks.
How CISM Professionals Support Vietnamese Enterprises
Information security managers help businesses make deliberate choices about technology risk. Their job is not simply to ask technical teams for additional security products. They must understand strategic priorities, identify important information assets, coordinate control ownership and ensure leaders receive timely information for decisions. During incidents, they are responsible for helping the organization maintain clarity when technical details remain uncertain.
Enterprise Challenges and CISM Capabilities
Enterprise challenge | CISM management capability | Potential practical result |
Unclear risk ownership | Governance and risk accountability | Recorded decisions and responsible owners |
Security budget disputes | Business cases and strategic alignment | Transparent prioritization |
Inconsistent supplier oversight | Third-party security program management | Better visibility of critical dependencies |
Weak incident escalation | Classification and communication arrangements | Faster coordinated decision-making |
Unverified recovery capability | Business impact and continuity planning | Realistic recovery priorities |
Limited board reporting | Management-relevant metrics | Clearer risk and progress visibility |
Practical Contributions of CISM Professionals
Establish an information security governance model that matches the enterprise.
Define risk appetite, policy ownership and escalation responsibilities.
Develop a security roadmap connected to business goals and budgets.
Set and monitor security controls, metrics and supplier expectations.
Coordinate incident response with communications, legal and operational stakeholders.
Support business impact analysis, continuity plans and recovery testing.
Present risk decisions and program performance to senior leadership.
These contributions are measurable only when supported by business leaders, clear accountability and continued review. Training can provide a common language, but governance improvement requires organizational decisions after the classroom ends.
CISM for Digital Transformation, AI, Privacy and Resilience in Vietnam
CISM Applications in Modern Enterprise Technology
Cloud services, API-connected business systems and remote access have increased the number of dependencies that a security manager must understand. CISM’s revised framework explicitly recognizes enterprise and information security architecture. Managers should know how important systems, trust boundaries, suppliers and business processes fit together before recommending controls or allocating investment.
Technology change | Security management question |
Cloud migration | Who owns configuration, monitoring, recovery and supplier risk? |
Digital payments | Which transaction risks require leadership attention? |
Industrial IoT | What level of service interruption is acceptable? |
Outsourced development | How are customer commitments translated into controls? |
AI-assisted workflows | Who approves data use, model access and incident handling? |
Managing AI-Enabled Security Risks
Security managers should approach AI with the same discipline used for other business-enabling technologies, while recognizing distinctive questions about data, model behavior, access and supplier dependencies. For example, an employee may upload confidential customer information to a public AI service. A management response requires policies, awareness, technical controls and incident escalation, rather than simply prohibiting all AI use.
CISM is not a specialist AI model development credential. Its value lies in establishing governance and accountability for the technology, choosing proportionate controls and asking whether the resulting residual risk fits the organization’s tolerance.
Privacy, Cybersecurity and the Vietnam Regulatory Environment
The 2026 effective dates of the Personal Data Protection Law and the consolidated Cybersecurity Law make current regulation an important topic for Vietnamese information security leaders. Organizations should map their actual data processing, contractual obligations, system classifications and sector requirements before asserting what compliance measures are necessary.
A CISM manager can coordinate the security-management response: identify affected assets, allocate policy owners, assess supplier risks, implement monitoring and connect incidents to legal and business escalation. Such management work should be conducted with qualified legal, privacy and technical specialists.
Business Continuity and Digital Resilience
Incident management accounts for 29% of the November 2026 CISM examination. It includes incident readiness, classification, communication, response and recovery, alongside business impact analysis and continuity and disaster recovery planning. The management challenge is to restore what matters most to the business while preserving appropriate evidence and stakeholder trust.
A financial services provider in Hanoi and a factory in Hai Phong will define critical services differently. Both should test roles and recovery decisions before an incident occurs. CISM preparation helps participants distinguish operational response from the executive decisions that enable it.
Security Governance for Agile, DevOps and Fast-Changing Systems
Security programs must accommodate rapid software releases and cloud infrastructure changes without losing clear ownership. Security managers need to know who approves exceptions, how control evidence is collected and whether significant changes alter enterprise risk. Working closely with DevOps and product teams allows security objectives to influence delivery early rather than appearing only at the final approval gate.
Benefits of CISM Certification for Professionals in Vietnam
CISM can help experienced professionals demonstrate that their security knowledge extends beyond tools and individual threats to enterprise decisions. The qualification is particularly relevant to roles that require managing budgets, teams, risk responses, security programs and incidents. Its value is strongest when the holder can describe real work aligned with those responsibilities.
Key Professional Benefits
Internationally recognizable ISACA information security management credential.
A management framework connecting security decisions to business priorities.
Stronger vocabulary for risk appetite, control ownership and executive reporting.
Structured knowledge of security architecture and program development.
Greater understanding of incident governance, continuity and recovery.
Support for career discussions in risk, GRC, security program and leadership roles.
A continuing education framework for maintaining management relevance.
CISM Skills for Different Professional Groups
Professional group | Useful CISM management emphasis |
Security operations leads | Escalation, incident governance and business impact |
IT risk and compliance professionals | Risk ownership and security decision-making |
Security architects | Strategy, control selection and enterprise alignment |
IT auditors | Transition from independent assurance to program accountability |
Technology managers | Resources, governance and supplier risk |
Prospective CISOs | Strategic reporting and enterprise resilience |
Professional benefits should not be presented as guaranteed promotions, salary premiums or automatic qualification for a management position. The CISM credential is awarded only after the individual meets ISACA’s certification requirements.
Benefits of Corporate CISM Training for Vietnamese Organizations
For enterprises, a CISM-aligned learning program can create a consistent approach to decisions that too often sit between departments. Security teams, enterprise risk managers, IT directors, continuity planners and compliance leaders benefit when their responsibilities are understood and documented. The course’s value depends on whether that shared understanding is translated into operating practices.
Corporate CISM Training Benefits by Department
Department / stakeholder | Potential business benefit |
IT and cybersecurity | Clearer security program roadmap and escalation |
Enterprise risk | Better documentation of cyber risk decisions |
Compliance and privacy | Security accountability to support compliance work |
Procurement and vendor management | Consistent assessment of critical third parties |
Operations and business continuity | Risk-informed recovery priorities |
Executive leadership | More meaningful security performance reporting |
Measuring Corporate CISM Training Effectiveness
Before delivery, corporate buyers should select a few measures tied to their existing problems. If the problem is unclear accountability, measure the percentage of material risks with owners. If incident exercises are weak, track findings and closure dates. If suppliers are poorly understood, measure review coverage among critical vendors. These indicators are more informative than course attendance alone.
Suggested measure | Baseline and follow-up method |
Risk ownership | Count significant risks without approved owners |
Security program execution | Review overdue remediation and decision logs |
Incident readiness | Compare exercise results and response actions |
Vendor governance | Measure completed critical supplier assessments |
Management reporting | Review consistency and timeliness of security metrics |
From Individual Learning to Organizational Security Capability
After a private corporate cohort, managers can agree on a focused action plan: review the security committee’s decision rights, refresh the risk register, run a supplier risk workshop, improve incident escalation or test one critical recovery scenario. A manageable set of outcomes is more likely to survive the training than a long list of unsupported aspirations.
Upcoming CISM Training Schedule in Vietnam
Spoclearn offers instructor-led CISM exam preparation for professionals and corporate teams across Vietnam. Upcoming public-batch dates, session times, instructor availability, delivery language and fees must be checked in the live training calendar or confirmed with the training advisor. No dates are published in this content master because a static document cannot confirm current batch inventory.
Training format | Duration | Location / arrangement | Action |
Live virtual public batch | 4 days / 32 hours | Vietnam-local timing, subject to schedule | View Training Schedule |
Private live virtual cohort | 4 days / 32 hours | Hanoi, Ho Chi Minh City and nationwide | Request Corporate Proposal |
Corporate on-site program | 4 days / 32 hours | Selected Vietnam location, by arrangement | Discuss On-site Delivery |
Enrollment checklist: confirm the updated 2026 CISM blueprint, trainer credentials, timings, materials, voucher inclusion and final commercial terms.
Build Stronger Information Security Leadership Across Vietnam
CISM Certification Training helps experienced professionals move from isolated security controls to enterprise-wide decisions about governance, risk, programs and response. Across Ho Chi Minh City, Hanoi, Da Nang, Hai Phong and Can Tho, Spoclearn’s four-day, 32-hour instructor-led course provides structured preparation for the current ISACA examination while encouraging practical application at work.
Choose a public training batch or request a dedicated corporate proposal that reflects your team’s responsibilities and business environment. ISACA independently administers and awards the CISM credential after its examination, experience and application requirements have been satisfied.
Where CISM Holders Drive Success
Request a Call Back from Spoclearn – We’re Just a Click Away
Got questions or need help choosing the right training or consulting solution? Schedule a call back with our expert team whenever you're able. Select a time that suits your schedule, and we’ll reach out to guide you through your options.