Why Digital Growth Is Raising the Importance of IT Audit
Vietnam’s digital economy is expanding across payments, e-commerce, online travel, business services and consumer applications. The government’s November 5, 2026 summary of the Google–Temasek–Bain e-Conomy SEA 2026 report projects approximately US$49 billion in digital-economy gross merchandise value (GMV) during 2026, a 20% increase year on year. This is a measure of transaction activity, not technology spending, job openings or a count of CISA professionals. It nevertheless illustrates how much commercial activity now depends on working digital systems.
More transactions, cloud workloads and system integrations increase the importance of identity controls, accurate processing, supplier assurance and operational recovery. An organization that can launch a new digital product must also be able to explain who approved changes, how access was granted, where data moved and what would happen after a major outage. Information systems audit turns those questions into an evidence-led assurance program.
2026 Regulatory and Cybersecurity Context
Vietnam’s Personal Data Protection Law No. 91/2025/QH15 took effect on January 1, 2026. The new Cybersecurity Law passed in December 2025 took effect on July 1, 2026. These changes make it especially important for enterprises to map data processing responsibilities and technology controls against applicable legal obligations. CISA does not qualify someone to provide a legal interpretation, but it supports the discipline needed to examine governance, access restrictions, data handling and monitoring.
A government-reported survey by Vietnam’s National Cybersecurity Association estimated approximately 552,000 attacks against information systems during 2025. This is a reported attack count, not 552,000 successful breaches. It is better used to demonstrate the need for careful risk assessment than to forecast audit hiring. Technology controls should be tested for effectiveness, not merely described in policy documents.
Verified reference point | Reported figure or date | What it means for IS audit |
Digital economy GMV projection | US$49bn in 2026 | Digital operations carry significant control dependencies |
Reported cyberattacks in 2025 | Approx. 552,000 | Need for risk assessment and tested defenses |
Personal Data Protection Law | In force Jan 1, 2026 | Privacy governance and control assessment |
New Cybersecurity Law | In force Jul 1, 2026 | Cybersecurity governance and control readiness |
Why IT Audit Matters to Vietnamese Enterprises
An IT audit should do more than produce a long list of missing settings. It should establish what can go wrong, whether management has selected reasonable controls and what testing supports a conclusion. Common weaknesses include excessive privileged access, unreviewed changes, unclear data ownership, vendor dependence, inadequate recovery testing and incomplete incident records.
CISA Career Opportunities Across Vietnam
CISA is best understood as an experienced-professional credential for information systems auditing and control. It is relevant where organizations need independent assessment of technology, risk or information security. An IT auditor may spend more time on evidence and reporting, while a cyber assurance specialist may examine technical control implementation. A governance professional may focus on board reporting, policies and third-party risk.
Relevant Career Opportunities
CISA Career Pathways Across Vietnam
Role | Typical accountability | Relevant Vietnam business centres |
IT / IS Auditor | Plan and test technology controls | Ho Chi Minh City, Hanoi |
Cyber Assurance Specialist | Evaluate security processes and evidence | Hanoi, Ho Chi Minh City, Da Nang |
Technology Risk Consultant | Review risk and control frameworks | Ho Chi Minh City, Hanoi |
Outsourcing Controls Lead | Assess SDLC and vendor obligations | Da Nang, Ho Chi Minh City |
Industrial IT Assurance | Examine production-system resilience | Hai Phong |
Digital Operations Auditor | Assess data and system reliability | Can Tho |
IT Audit Manager | Lead engagements and communicate findings | Hanoi, Ho Chi Minh City |
Career Progression Beyond CISA
CISA can help professionals demonstrate depth in IS audit principles, but career growth comes from successfully handling difficult assignments. A senior auditor must know when evidence is inadequate, how to challenge a control owner respectfully, and how to explain a material risk without exaggeration. At management level, responsibilities expand to audit planning, resourcing, quality review and communication with executive stakeholders.
Possible development routes include head of IT audit, internal audit director, technology risk director, privacy assurance lead, cloud assurance specialist and consulting leadership. Depending on career goals, CISM, CRISC, CGEIT or specialist cloud and privacy qualifications may complement CISA. These are related skills, not automatic promotions or requirements for every job.
Industries Requiring Information Systems Audit Capabilities in Vietnam
Technology-related controls matter well beyond software companies. Banks need reliable transaction processing, manufacturers depend on industrial systems, retailers handle customer information, and logistics providers depend on accurate inventory and tracking. CISA principles can support assurance in all of these environments, although audit objectives should reflect the actual business risks.
Industry | Illustrative audit focus | Relevant locations |
Banking and financial services | Core banking controls, access, transaction integrity | Hanoi, Ho Chi Minh City |
Fintech and payments | Application security, APIs, incident response | Ho Chi Minh City, Hanoi |
IT outsourcing and software | SDLC controls, customer data, supplier assurance | Da Nang, Ho Chi Minh City |
Telecommunications | Network changes, service continuity, privacy | Hanoi, Vietnam-wide |
Manufacturing | ERP, operational technology, backup recovery | Hai Phong |
Logistics and ports | Systems availability, vendor access, data interfaces | Hai Phong, Can Tho |
E-commerce and retail | Identity, payment controls, customer data | Ho Chi Minh City |
Healthcare | Clinical data, system availability, access controls | Hanoi, Ho Chi Minh City |
Hospitality and tourism | Booking systems, data protection, business continuity | Da Nang |
Agriculture and food processing | Traceability and inventory-system integrity | Can Tho |
Professional services | Client confidentiality, outsourced IT controls | Hanoi, Ho Chi Minh City |
Selecting the Right Audit Approach
There is no single audit checklist that fits all systems. A well-established payroll application may require access, change and interface tests; a cloud-native product may need infrastructure configuration evidence and provider responsibility mapping. A factory-control system may demand greater emphasis on availability, safety dependencies and controlled maintenance windows. The audit approach should reflect risk, business context and reliable evidence rather than a fixed sequence of technical tests.
CISA Certification Opportunities Across Vietnam’s Major Cities
CISA Certification Training and IT Audit Careers in Ho Chi Minh City
Ho Chi Minh City is a major centre for banking, fintech, multinational services, technology, retail and digital commerce. As the wider administrative and industrial region has developed, assurance work also spans manufacturing, distribution and port-related systems. For auditors, the central challenge is often the interaction between cloud platforms, customer-facing applications, payment services and third-party providers.
Business environment | Typical audit assignment | Relevant CISA capability |
Digital payments | API access and reconciliation review | Control evidence and integrity |
Retail / e-commerce | Customer data and identity review | Information asset protection |
Multinational groups | Shared-service and vendor assurance | Governance and third-party risk |
Industrial operations | ERP and recovery testing | Business resilience |
Consider an e-commerce payment gateway linked to several processors. An auditor should establish which party is responsible for authentication, how exceptions are handled and whether transaction reconciliation is complete. Vendor assurances may help, but they do not remove the need to verify controls within the client’s scope. In a multinational environment, reports must also be intelligible to reviewers outside Vietnam.
CISA Certification Training in Ho Chi Minh City is relevant to IT auditors, GRC consultants, security assurance professionals and technology risk managers seeking structured preparation. Adecco’s 2026 guide reports occupational pay ranges for internal audit managers, but these should not be described as CISA-only salaries. [10]
CISA Training and Governance Careers in Hanoi
Hanoi brings together banking, government administration, telecommunications, enterprise technology, education and large professional-services operations. These environments may demand formal evidence of risk ownership, authorization, access reviews and continuity planning. Audit findings are most effective when they connect technical deficiencies to an operational or regulatory consequence.
Sector | Illustrative risk or control | Audit focus |
Banking | Privileged access to critical platforms | Approval, logging and recertification |
Telecommunications | Network configuration changes | Change authorization and rollback |
Public services | Large sensitive-data repositories | Governance, classification and access |
Enterprise IT | Vendor-managed cloud services | Shared responsibilities and assurance |
A bank migrating workloads to a new platform may have a complete project plan and still lack convincing evidence that critical access rights were reviewed before go-live. The auditor needs to ask about business approval, migration testing, logging and the recovery approach. CISA connects that technical review with project governance and evidence quality.
For professionals pursuing CISA Certification Training in Hanoi, strong career applications include financial services IT audit, enterprise technology risk, public-service system assurance and internal audit management. Familiarity with Vietnam’s active data-protection and cybersecurity framework remains necessary alongside ISACA’s global standards.
CISA Certification Training and Technology Assurance in Da Nang
Da Nang’s software outsourcing, digital services, hospitality and technology operations create opportunities for professionals who can evaluate controls supporting international client work. System development procedures, customer-data segregation, incident escalation and outsourced cloud dependencies can be more significant than traditional infrastructure ownership.
Operating model | Assurance challenge | Related CISA topic |
International software delivery | Approved code changes and release traceability | Systems development controls |
Managed cloud services | Provider versus customer responsibility | IT governance and asset protection |
Tourism platforms | Customer data and transaction continuity | Privacy and resilience |
Service operations | Incident response and evidence retention | Operations and audit execution |
A software provider may have strong engineering practices but incomplete segregation of developer access from production deployments. An auditor should inspect the documented process, sample changes and determine whether exceptions are approved and reviewed. A policy stating “four-eyes approval” is not evidence that reviews actually occurred.
CISA training in Da Nang is suitable for professionals moving from engineering, QA or information security into technology assurance roles. Candidates should pay particular attention to audit methodology, independence and report writing if their previous duties concentrated on designing or operating systems rather than evaluating them.
CISA Certification Training and Industrial IT Audit in Hai Phong
Hai Phong’s manufacturing, logistics, port and industrial activity makes operational reliability a central technology risk. A factory may use enterprise resource planning software, programmable equipment, vendor-managed networks and specialized maintenance tools. Outages or unauthorized changes can affect production capacity as well as data confidentiality.
Industrial activity | Illustrative assurance question | CISA domain application |
Factory automation | Who can modify operating settings? | Protection of information assets |
Supplier maintenance | Is remote access time-bound and logged? | IT governance and security |
ERP / inventory | Are interfaces reconciled reliably? | System operations |
Plant continuity | Can backups restore critical applications? | Business resilience |
Suppose a production line depends on a supplier with permanent remote access to a control workstation. An effective audit considers contractual obligations, authorization, monitoring, emergency access and the effect of disconnecting the vendor during an incident. The right recommendation may require input from safety, engineering and production teams.
CISA Certification Training in Hai Phong can be relevant to industrial IT teams, internal auditors, ERP control specialists and risk managers. It complements, but does not replace, specialist operational technology engineering and safety expertise. Real audit competence involves understanding how controls behave during actual operating conditions.
CISA Certification Training and Digital Control Opportunities in Can Tho
Can Tho is an important Mekong Delta centre for food processing, agriculture-related commerce, distribution, logistics and regional services. Digital control requirements often arise from stock traceability, temperature-sensitive storage, finance platforms and connectivity between production facilities and warehouses.
Business system | Potential risk | Audit priority |
Warehouse management | Incorrect stock and movement records | Interface and reconciliation testing |
Cold-chain monitoring | Incomplete sensor data | Integrity and exception handling |
Food traceability | Uncontrolled record changes | Identity and audit logs |
Distribution systems | Interruption of regional services | Recovery planning and vendor support |
Imagine a food processor transferring traceability records between a production application and a warehouse system. The auditor should evaluate whether all records transfer, how failures are detected and which employee investigates discrepancies. Testing a few successful transactions is not enough if error handling is weak.
CISA training in Can Tho helps operations auditors, IT managers and compliance practitioners develop a stronger assurance perspective. Career opportunities should be assessed against actual local vacancies and enterprise needs rather than inferred from regional economic activity. The core skill remains asking the right risk question and collecting defensible evidence.
How CISA Professionals Support Vietnamese Enterprises
Information systems auditors help organizations determine whether technology controls provide reasonable assurance over important business objectives. Their role is not to operate every security tool or approve every project decision. It is to understand risks, review the control environment, test evidence and report gaps in language management can act upon.
In a Vietnamese enterprise, IT audit may work with the board audit committee, internal audit, cyber security, compliance, finance, product owners and external service providers. Effective assurance protects independence while maintaining practical knowledge of how the organization actually runs.
Enterprise Challenges and CISA Capabilities
Enterprise challenge | Audit capability | Potential outcome |
Unclear privileged-access ownership | Access control testing | Better visibility of unauthorized permissions |
Insufficient change evidence | Sampling and change-control review | More reliable production change process |
Fragmented vendor assurance | Third-party risk review | Clearer residual-risk ownership |
Untested recovery arrangements | Review of BIA, backup and DR evidence | More credible recovery readiness |
Privacy control weaknesses | Data governance and processing-control review | Stronger understanding of compliance gaps |
Inconsistent audit reporting | Risk-based finding and communication | Actionable management decisions |
Practical Contributions of CISA Professionals
CISA is a professional benchmark for these capabilities, but the usefulness of any audit depends on management access, organizational independence, sound sampling, trustworthy evidence and the auditor’s actual experience.
CISA for Digital Transformation, AI, Privacy and Resilience in Vietnam
As Vietnamese enterprises modernize, audits increasingly cover systems that cross departmental and supplier boundaries. A new cloud platform may sit alongside legacy databases; an AI-enabled workflow may consume customer information; a manufacturing operation may introduce connected machinery. These developments change where evidence is found and who is accountable for control operation.
CISA Applications in Modern Enterprise Technology
Technology development | Illustrative audit emphasis |
Cloud and SaaS | Shared responsibility, identity, configuration and logging |
AI-supported decision processes | Data quality, governance, human oversight and traceability |
Digital payments | Transaction integrity, fraud controls and resilience |
Agile / DevOps delivery | Release approvals, automated testing, deployment access |
Industrial IoT | Asset identification, maintenance access, availability |
Cross-border data flows | Classification, transfer responsibilities and monitoring |
Auditing AI-Enabled Processes
AI tools can help auditors search large evidence sets, classify documents or identify unusual transactions. They can also produce incorrect summaries or miss context. An auditor should understand the data source, validation process, access controls, change history and level of human review. Automated confidence scores should not be mistaken for independently verified audit evidence.
In Ho Chi Minh City and Hanoi, AI-enabled services may appear in banking, customer support and enterprise platforms. Da Nang software providers may build AI-assisted workflows for overseas clients. CISA gives a framework for examining governance and control responsibilities; specialized AI audit techniques require additional practical training where appropriate.
Privacy, Cybersecurity and the Vietnam Regulatory Environment
The Personal Data Protection Law and the new Cybersecurity Law give Vietnamese businesses additional reasons to examine data inventory, access, supplier relationships, information retention and incident management. Auditors should coordinate with qualified legal and compliance professionals to interpret what applies to a particular processing activity. CISA preparation contributes testing discipline, not a blanket certification of statutory compliance.
Business Continuity and Digital Resilience
Disaster recovery planning is useful only when the organization can demonstrate that recovery steps and restoration times are realistic. Auditors may inspect the business impact analysis, recovery objectives, backup integrity, test results and unresolved findings. In a bank, downtime threatens transactions; in a factory, it can stop production; in logistics, it can interrupt traceability and delivery.
Auditing Predictive, Agile and DevOps Delivery
Different technology delivery methods create different control evidence. A traditional system implementation may use formal milestone sign-offs. An Agile team may maintain automated approval trails, tested code branches and continuous deployment logs. CISA auditors should assess whether these mechanisms meet control objectives, not require every team to use the same paperwork. The question is whether management can demonstrate appropriate approval, testing, segregation and recovery capabilities.
Benefits of CISA Certification for Professionals in Vietnam
CISA provides an internationally recognized way for experienced practitioners to demonstrate assessed knowledge of information systems audit, governance and controls. It supports professional credibility across industries with technology-dependent processes. The strongest career benefits appear when exam preparation is combined with substantial audit experience, clear writing and sound judgment.
Key Professional Benefits
CISA Skills for Different Professional Groups
Professional group | Practical value of training |
Internal auditors | Evaluate automated and technology-dependent controls |
Cybersecurity practitioners | Assess evidence of security control effectiveness |
IT managers | Understand assurance expectations and ownership boundaries |
Accountants and assurance teams | Connect financial-control objectives with IT general controls |
Risk and compliance professionals | Evaluate IT governance and third-party risk |
Technology consultants | Communicate control findings to international clients |
Participants should choose CISA according to their actual responsibilities and career direction. The course helps build knowledge; ISACA certification and enterprise-level competence require additional steps and professional experience.
Benefits of Corporate CISA Training for Vietnamese Organizations
Enterprises benefit when audit, technology and risk teams can evaluate controls in a consistent, disciplined way. A shared foundation can reduce confusion about evidence sufficiency, remediation responsibility and the difference between policy compliance and actual control operation. Corporate cohorts can also compare audit approaches across locations and departments.
Corporate CISA Training Benefits by Department
Department | Potential organizational benefit |
Internal audit | Better scoped, evidence-led technology audits |
Information security | Independent assessment of security control performance |
IT operations | Clearer audit requirements and remediation ownership |
Risk and compliance | More consistent governance and risk reporting |
Finance | Stronger assessment of systems supporting financial data |
Procurement and vendors | Improved third-party control review |
Measuring Corporate CISA Training Effectiveness
Measurement should begin before training. Review the quality of current audit workpapers, the extent of evidence rework, repeated high-risk findings, remediation delays and stakeholder feedback. Afterward, ask whether auditors identify the real cause of problems, distinguish control design from operating effectiveness and produce reports that decision-makers understand.
Measurement area | Example performance indicator |
Audit methodology | Consistency of risk assessment and sampling |
Documentation | Percentage of workpapers requiring rework |
Reporting | Findings supported by clear condition, cause and impact |
Remediation | Closure quality for major control deficiencies |
Professional development | Domain assessment and certification progress |
From Individual Learning to Organizational Audit Capability
A training program becomes more valuable when leaders give employees time to apply it. Organizations might refresh audit programs, improve risk registers, introduce peer review of workpapers and conduct follow-up testing on completed corrective actions. Audit committees and senior managers should reinforce accountability without asking auditors to become control owners. Sustained improvement depends on practice and governance, not a certificate alone.
Upcoming CISA Training Schedule in Vietnam
Spoclearn’s public and private CISA training arrangements should be displayed through the live course schedule rather than fixed dates copied into an evergreen Vietnam landing page. The training duration is four days / 32 hours. Start dates, local time, language and instructor availability must be confirmed before publication or payment.
Schedule field | Publishing recommendation |
Upcoming dates | Populate dynamically from Spoclearn booking system |
Session duration | 4 days / 32 hours |
Time zone | Vietnam time (ICT, UTC+7) for local cohorts |
Delivery mode | Live virtual; private on-site by corporate proposal |
Training language | English |
Exam voucher | Included with Training Cost |
Enrollment CTA | View Training Schedule / Request Corporate Training |
Build Stronger IT Audit and Digital Trust Capabilities Across Vietnam
Spoclearn’s CISA® Certification Training in Vietnam helps auditors, governance professionals and corporate teams prepare for ISACA’s Certified Information Systems Auditor examination while improving their approach to technology control assessment. In four instructor-led days, participants examine audit methodology, governance, implementation risks, operational resilience and information protection through practical examples.
The Vietnam country page supports professionals in Ho Chi Minh City, Hanoi, Da Nang, Hai Phong and Can Tho, with industry contexts spanning banking, fintech, outsourcing, manufacturing and logistics. Individuals can review training schedules and available package details; organizations can request private group sessions, location-specific delivery and case-based customization.
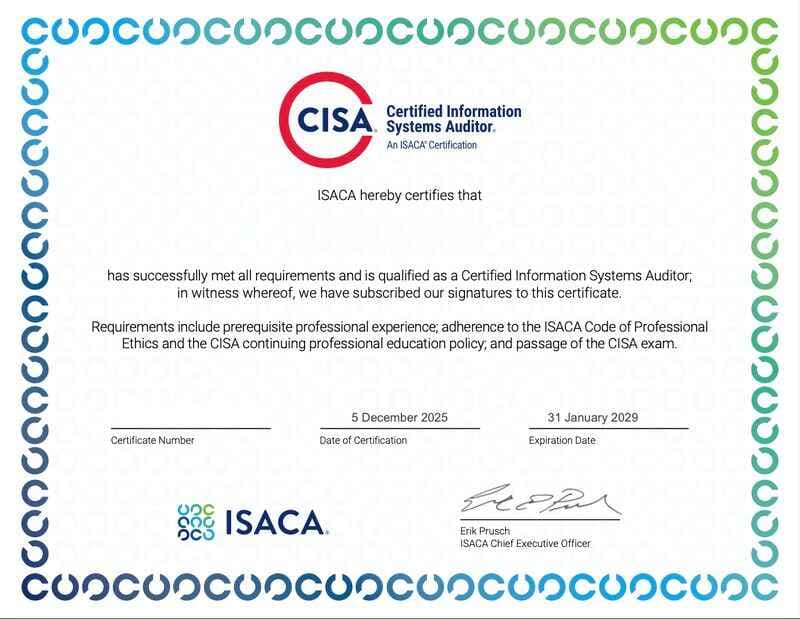
ISACA awards CISA certification only after applicable examination and experience requirements are met. Spoclearn training does not itself confer the CISA credential. Strengthen your assurance judgment, improve the clarity of control findings and build capabilities that support trustworthy digital operations.

 CN
 CN
 CN
 CN