CRISC Certification Training in Japan
 CN
 CN
 CN
 CN
Enhance enterprise IT risk management, cybersecurity governance, and information systems control capabilities with Spoclearn’s CRISC Certification Training in Japan. Aligned with ISACA standards, this instructor-led program equips professionals and enterprise teams for advanced roles in IT risk, governance, audit, compliance, and cybersecurity through Japan-focused case studies and structured exam preparation. Delivered via live online sessions across Japan, including Tokyo, Osaka, Yokohama, Nagoya, Fukuoka, Sapporo, Kobe, Kyoto, Hiroshima, and Kawasaki, this training enables learners to gain globally recognized CRISC expertise and drive risk-aware, compliant decision-making in highly regulated and technology-driven industries.

CRISC® CURRICULUM: COMPLETE COURSE SYLLABUS & LEARNING PATH
Who Can Attend CRISC Training in Japan
Job roles that can take up CRISC training course include, but are not limited to:
- Business Analysts
- Risk Professionals
- Project Managers
- IT Professionals
- Chief Risk Officers (CROs)
- IT Audit Specialists
- Security Analysts
- Risk Consultants
- Compliance Officers
- Control Professionals
- Compliance Professionals
- Audit Managers
- IT Security Managers
- Governance Professionals
- Enterprise Risk Managers
- Operations Managers
- Chief Information Officers (CIOs)
- Anyone who manages a company’s IT risks and controls
What is CRISC Exam Pattern and Question Format?
- Exam Type: Multiple-Choice Questions
- No. of Questions: 150
- Duration: 4 Hours (240 Mins)
- Passing score: 450 or Higher out of 800
- Languages: English, Chinese Simplified, Spanish, Korean.
CRISC® Course FAQ's
CRISC Certification Course in Japan
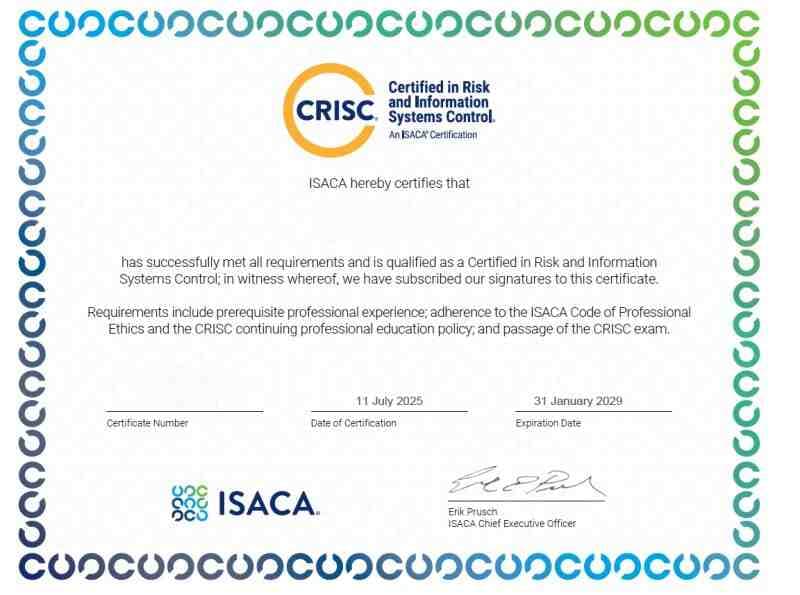
Certified in Risk and Information Systems Control (CRISC) credential, governed by ISACA, is one of the world’s most respected certifications for professionals responsible for identifying, assessing, responding to, and monitoring enterprise IT risk. In Japan, CRISC is highly relevant as organizations manage advanced digital transformation initiatives, including cloud adoption, AI integration, ransomware risks, supply chain dependencies, OT/IoT security, regulatory compliance, and operational resilience across complex enterprise environments.
Spoclearn’s CRISC Certification Course in Japan is aligned with ISACA’s official exam framework while contextualizing learning for key Japanese industries such as banking, insurance, manufacturing, automotive, electronics, telecom, healthcare, public sector, logistics, retail, consulting, energy, and technology. The CRISC exam includes 150 questions covering four domains: Governance, Risk Assessment, Risk Response and Reporting, and Information Technology and Security. Delivered through live online training across Japan and corporate classroom sessions in major business hubs like Tokyo, Osaka, and Yokohama, the program supports both individual career growth and enterprise-wide GRC capability development. It is ideal for IT auditors, cyber risk professionals, compliance managers, cloud governance specialists, information security leaders, and enterprise risk consultants looking to align technology controls with business resilience, regulatory expectations, and strategic risk decision-making.
Spoclearn: Training That Works for Corporates
Get tailored training programs for individuals and enterprise teams that help to maximize your training budgets
Customized training solutions designed to meet individual and organizational goals for maximum effectiveness.
Learn from 200+ global experts with real-world industry experience and proven expertise.
Blended training options to suit diverse learning preferences and geographically dispersed teams.
Post-training coaching ensures the practical application of skills for measurable, lasting results.
What Makes Spoclearn Different
Growing Demand for CRISC Professionals in Japan
Request a Call Back from Spoclearn – We’re Just a Click Away
Got questions or need help choosing the right training or consulting solution? Schedule a call back with our expert team whenever you're able. Select a time that suits your schedule, and we’ll reach out to guide you through your options.